Blog

Evaluate Internet Sources Using Structured Approach to Research and Communicate Process to Doctoral Students

Evaluate Internet Sources Using Structured Approach to Research and Communicate Process to Doctoral Students


Evaluate Internet Sources Using Structured Approach to Research and Communicate
Process to Doctoral Students

During Week 1, we examined two types of publications. This week, we turn our focus
toward how to examine resources located on the Internet. Internet searches are much
easier than electronic library searches, but Internet searches present challenges.
For example, many people are not qualified to present objective information, and
they post inaccurate or biased information. The locations can be informal, such as
personal blogs; or they can be more formal, such as on professional organization
websites. The challenge for professional and academic researchers is to ensure the
information retrieved and relied on is accurate and free from excessive bias. This
week, you will practice locating resources on the Internet and analyzing
information for credibility, and creating a presentation to help other doctoral
students evaluate Internet sources.

For this task, begin by locating at least three sources of information from
Internet resources on a business topic of interest to you. The information should
be from a professional organization website or from a website specializing in a
particular subject. Ensure there is an author identified and be sure the
qualifications of the author are presented in the website information.

Next, imagine that you will be creating a PowerPoint Presentation to doctoral
students to help them evaluate sources. Create a visual diagram that reflects the
process steps students need to go through to evaluate Internet sources. Explain
each of the steps in the process in detail and use the three sources you identified
as examples. Be sure to consider the following questions to help your doctoral
student audience understand the validity of the authors you researched.

Who is the author?
What are the main points the author is presenting?
What are the author’s educational and experience credentials? In what way do they
support the author’s ability to express an opinion on the subject?
Has the research been peer-reviewed or gone through an editorial process?
What types of bias may be present?
Who has a contrary opinion on the subject, and what are their credentials?
How old is the material, and is it still relevant?
End your PowerPoint presentation by providing a real-life example from a specific
business context where you could apply the Internet source evaluation process you
just developed to promote a specific business improvement idea to your management
team. How might the source evaluation process help you build credibility in a
business setting? How is the source evaluation process different in academia verses
a business context?

Incorporate appropriate animations, transitions, and graphics as well as speaker
notes for each slide. The speaker notes may be comprised of brief paragraphs or
bulleted lists.

Support your presentation with at least 3 scholarly resources. In addition to these
specified resources, other appropriate scholarly resources may be included.

Length: 9-12 slides (with a separate reference slide)

Notes Length: speaker notes of 200-350 words per slide.

Be sure to include citations for quotations and paraphrases with references in APA
format and style where appropriate. Save the file as PPT with the correct course
code information

Explain the features of secure e-mail

Explain the features of secure e-mail

A company in Manhattan still keeps to the traditional mailing approaches even though the nature of their business strictly involves confidential documents that need to be sent to clients. Tell this Manhattan Company why you think their messages can be securely sent to clients using e-mail.

Write a 2-3 page e-mail that includes the following:

Explain the features of secure e-mail and how secure e-mail works.
As a good consultant, make sure that they are also aware of the vulnerabilities involved in e-mail communication and how they can be countered.
Your paper should be written in the APA style, and should cite any sources you used.

Price discrimination strategy of united airlines

Price discrimination strategy of united airlines

Price discrimination strategy of united airlines

Macroeconomics
Price Discrimination: Suppose that United Airlines knows that it faces the
following demand equations and corresponding marginal revenue equations for its
(one-way) SFO to Las Vegas route:

Friday Departure: P = 320-2Q (Demand)

MR = 320-4Q (Marginal Revenue)

Tuesday Departure: P = 200-Q (Demand)

MR = 200-2Q (Marginal Revenue)

Marginal Cost is a constant $40 per passenger.

a) Find the profit-maximizing quantity of passengers for Friday departures and
Tuesday departures. Find the profit-maximizing price for each.

b) Calculate total revenue received on Friday flights and Tuesday flights.

c) Draw two separate graphs for Friday demand and Tuesday demand. In your graph
include a marginal revenue curve and marginal cost curve. Show the profit
maximizing price and output for each graph.

d) What if United Airlines charged $150 per passenger everyday of the week, would
this maximize profits? Why or why not?


How software vulnerabilities can be exploited

How software vulnerabilities can be exploited

Objectives:

The main objective of this assignment is for the students to understand the security mechanisms in Unix-like operating systems and their interplay with software security, in particular:

– to learn practical access control mechanisms in Unix operating system, such as files and folder permissions and SUID programs, and how application security is affected by them;

– to learn how software vulnerabilities can be exploited to circumvent security mechanisms in both applications and operating systems.

Problem Description:

There are three problems in this assignment. To do this assignment, you will make use of an installation of Ubuntu Linux 12.04 (32 bit) in the Oracle VirtualBox virtual machine. The VirtualBox image of the Ubuntu installation is provided with this document and can be downloaded from the NTULearn site for this assignment, under the Group assignment menu. The assessment of the solutions to the problems listed below will be entirely done inside this particular installation of Ubuntu.

The Ubuntu installation for this assignment is a clone of the Ubuntu image provided for the tutorial sessions. In particular, it has the following users: admin, alice, bob, charlie, dennis, eve and fong.

User admin has the administrative privilege over the system, i.e., it can escalate its privilege to the root user.

The user bob maintains several applications that allows a user to access a certain ‘secret’, when the right password is provided. These passwords are different from the user account passwords. To distinguish the two, we shall call these passwords as application passwords. Every user is assigned a unique secret and a unique application password. The secrets take the form of a string of alpha numeric characters. The application passwords and the secrets are stored in individual files. The locations for these files are summarized in Table 1. The application passwords are strings of lower- case letters, of length at most 14 characters.

IMPORTANT NOTE: Appendix A provides the account passwords, the application passwords and the secrets for all users. All these passwords and secrets, except those for user ‘charlie’, will be changed during the assessment of your solutions. So your solutions must not hardcode any of these passwords and secrets other than charlie’s.

User name Application password file location Secret file location
admin /home/admin/Private/password /home/admin/Private/secret
alice /home/bob/Private/alice/password home/bob/Private/alice/secret
bob /home/bob/Private/bob/password home/bob/Private/bob/secret
charlie /home/bob/Private/charlie/password home/bob/Private/charlie/secret
dennis /home/bob/Private/dennis/password home/bob/Private/dennis/secret
eve /home/bob/Private/eve/password home/bob/Private/eve/secret
fong /home/bob/Private/fong/password home/bob/Private/fong/secret

Table 1. Locations of application passwords and secrets. Each password is stored in a file called ‘password’, and each secret is stored in a file called ‘secret’.

There are three main programs that a user can use to display his or her secret:

– user-secret: This program is used to access the secrets for the following users only: alice, charlie, dennis, eve and fong. It takes two arguments: a user name and an (application) password. If the application password supplied is correct for that user, the secret for the user will be displayed. The following screenshot shows an example of the output of a normal run of the program.

– bob-secret: This program is used by user bob to access his secret. It takes one argument, which is bob’s application password. If the password is correct, bob’s secret will be displayed. The following screenshot shows an example of the output of a normal run of the program.

– admin-secret: This program is used by user admin to access its secret. It takes one argument, which is admin’s application password. If the password is correct, admin’s secret will be displayed. The following screenshot shows the output of a normal run of the program.

In addition to the above three programs, there are additionally two helper programs:

– show-secret: This program is invoked by bob-secret to display bob’s secret, in case of a successful authentication check. It is not supposed to be invoked by the users directly.
– register: This program is invoked by bob-secret to display an error message in case of an unsuccessful authentication check. It is not supposed to be invoked by the users directly.

All of the above programs, except for register, are SUID programs. Table 2 lists the locations of the binaries of the programs. The source code of these programs are written in C and are located in the same directory as their binaries. For your convenience, the source code of these programs are included in Appendix B.

There are further details about the permissions of each program above that you need to discover on your own. Pay particular attention to the SUID programs and their owners.

Table 2. Program locations

There are 3 (three) problems you need to solve for this assignment. For each problem, you are asked to write an attack program or script. These attack programs/scripts must be executed using user charlie’s account. So in the following, we assume all attack programs/scripts are located in
/home/charlie/.

Problem 1

Your first task is to write an attack script or a program to display the secret of any of the following users: alice, charlie, dennis, eve, or fong. The attack program takes one argument, which is the user you want to attack. The attack must work when executed by user charlie. If your program/script works correctly, it should show something that looks like the following:
1012_figure.jpg

That is, each successful attack should display the word ‘Secret: ‘, followed by a string that is the secret.

Problem 2

For this problem, you are asked to write an attack script/program to display bob’s secret. The attack program takes no argument. As in Problem 1, this attack must work when launched by user charlie. The following screenshot shows what a successful attack should look like:
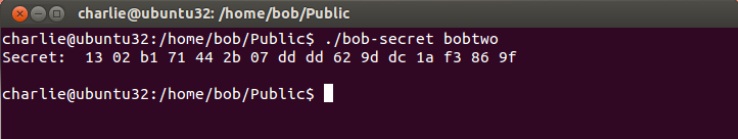
1821_figure1.jpg

Problem 3

For Problem 3, you are asked to write a script/program to display the application password and the secret of the admin user. The attack program takes no argument. A successful attack should output something like the following:
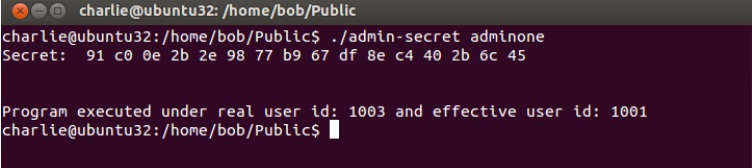
1754_figure2.jpg

Again, as in previous problems, this attack must be successfully executed when logged in as charlie.

The attack should output two lines: the first one contains the application password (the line prefixed by ‘Password:’) and the second one contains the secret of the admin user (the line prefixed with ‘Secret:’).

Assessment

The assessment is based on two components:

1. Attack code execution: This is broken down to 15% for Problem 1, 15% for Problem 2 and 20% for Problem 3. The assessment of the correctness of your attack will be partially automated, so please make sure you follow the suggested output format as mentioned in the problem description above. Your solutions will be tested in the same virtual machine that is provided with this assignment, but with all password and secret values modified (except for charlie’s passwords and secret). So you should make sure that you do not hardcode any of the sample passwords/secrets, other than charlie’s, mentioned above in your solutions, as they will not work in the assessment process. Each attack must be successfully executed within 2 (two) minute. This is really a gross approximation; if you implement the attacks correctly, each attack should take only a few seconds to solve the given problem.

2. Report- There is no definitive structure of the report, but here are some guidelines of what we would expect from the report:

– As a general guideline we expect a division into three parts, corresponding to the division of the problems. But if you are able to find a single attack that solves all problems, in which case, the division per problem does not work so well and the report will be judged more holistically.

– We expect a detailed analysis of what are the vulnerabilities and how you exploit them. It is not enough, for example, to say that you do a ‘stack overflow’ attack. You’d need to explain about the memory layout, what is the effect of the overflow, how do you subvert the control flow of the program, etc. Similarly, where the problem/solution concerns Unix security mechanism, I expect you to articulate clearly the aspects of the control mechanism that cause the vulnerability, and how you exploit them.

Explain the necessary components within a security policy

Explain the necessary components within a security policy

Remote Access Security Policy

Organization: XYZ Health Care Provider:

XYZ Health Care is a provider of health services to senior citizens. It performs its mission with a virtual force of Registered Nurses and Nurse Practitioners. The nurses visit their elderly patients in their homes and monitor their health. At the end of the day, the nurses are required to connect back to corporate networks and upload all of the patient records for the day. Keep in mind that this organization is subjected to HIPAA rules and its required to make the data available to its patients and authorized patient representatives within 48 hours.

Some of the RISKS:

• Brute force user ID and password attacks
• Users or employees unaware of the risks, threats, and dangers of the Internet and shard WI-FI or broadband Internet Access
• Multiple Access attempts and logon retries
• Unauthorized access to IT Systems, applications, and data
• Privacy data or confidential data is compromised remotely
• Data leakage occurs in violation of data classification standard
• A remote worker’s laptop is stolen
• A remote worker requires access to the patient medical records system through the Public Internet

Scope: Control Identification and Creation of a Remote Access Policy

Using or textbooks, internet and other resources, identify the necessary components / sections within a security policy and then craft the actual policy for XYZ Healthcare and address the risks within policy that are prevalent with Remote Access.

Your submission must include the following:

1) Control Matrix: A listing of the risk and 1 or more countermeasure to address the risk.

2) A Section that identifies the necessary components of the policy and why they are important: This does not refer to the controls but more specifically sections within the policy. (You may research the Internet or SANS for sample policies, the sections were also discussed in class).

3) The actual policy, when developing the policy please ensure that it can be used at XYZ Healthcare.

4) Based on the white paper provided? What are the four goals of effective metrics as defined in the paper. In your own words explain your understanding of the metric and where and how it can be beneficial.

Paper Requirements

1) APA Format (Where applicable)
2) Minimum of 3 – 5 references
3) Safe – Assignment comparison will be done

Relationship between infrastructure and security

Relationship between infrastructure and security

This assignment consists of two (2) sections: an infrastructure document and a revised Gantt chart or project plan.

The infrastructure which encompasses the network solution and security considerations is a major consideration for your company. Considering that the company will be expanding from one (1) floor to three (3) floors in the very near future you, as the CIO, are responsible for the design of the infrastructure and security protocols. You have been tasked with designing a network that is stable, redundant, and scalable. In addition, speed and reliability are important considerations. Assumptions should be drawn regarding network usage in relationship to network services and resources. All the established criteria that were set at the onset should be adhered to within your plan. The network solution that is chosen should support the conceived information system and allow for scalability. The network infrastructure will support organizational operations; therefore, a pictorial view of workstations, servers, routers, bridges, gateways, and access points should be used. In addition, access paths for Internet access should be depicted. Additionally, the security of the network should be in the forefront of your design because protecting your data is a primary consideration.

Section 1: Infrastructure Document

Write a four to six (4-6) page infrastructure document in which you:

1. Justify and support the relationship between infrastructure and security as it relates to this data-collection and analysis company.

2. Present the rationale for the logical and physical topographical layout of the planned network.

3. Design a logical and physical topographical layout of the current and planned network through the use of graphical tools in Microsoft Word or Visio, or an open source alternative such as Dia. Note: The graphically depicted solution is not included in the required page length.

4. Illustrate the possible placement of servers including access paths to the Internet, intrusion detection systems (IDS), and firewalls.

5. Create and describe a comprehensive security policy for this data-collection and analysis company that will:

Protect the company infrastructure and assets by applying the principals of confidentiality, integrity, and availability (CIA). Note: CIA is a widely used benchmark for evaluation of information systems security, focusing on the three (3) core goals of confidentiality, integrity, and availability of information.

Address ethical aspects related to employee behavior, contractors, password usage, and access to networked resources and information.

Section 2: Revised Project Plan

Use Microsoft Project to:

Update the project plan from Project Deliverable: Analytics, Interfaces, and Cloud Technology, with three to five (3-5) new project tasks each consisting of five to ten (5-10) sub-tasks.

Identify at least five potential causes of network failure

Identify at least five potential causes of network failure

Computer Science

Networks are not perfect, and errors will occur because of software and hardware problems. Network downtime is costly to business operations and should be minimized where economically possible. Part of the Network Improvement Plan consists of reduction of network problems and downtime through the implementation of a solid fault tolerance plan.

For this assignment, you will develop a Fault Tolerance Plan section to add to the overall Network Improvement Plan document.

The project deliverables for this Week are as follows:

• Update the Network Improvement Plan document title page with the new date.
• Update the previously completed sections based on the instructor’s feedback.
• Fault Tolerance Plan

o Identify at least 5 potential causes of network failure.
o For each potential cause of network failure, create a plan with the necessary steps and required hardware to reduce the risk of failure.
o Include the cost and benefit comparison for each risk reduction plan to justify the plan.

Explain type of services provided by a financial institution

Explain type of services provided by a financial institution

Explain type of services provided by a financial institution


Macroeconomics
Carson Company is attempting to compare their services offered by different banks
as it would like to have all services provided by one bank.

a) Explain the different types of services provided by a financial institution that
may allow Carson Company to obtain funds or to hedge its risk.

b) Review the service s you listed in the previous question. What services could
provide financing to Carson Company? What services could hedge Carson’s exposure to
risk?

Explaining characteristic of san or a nas configuration

Explaining characteristic of san or a nas configuration

1. Storage Area Networks (SAN) and Network Attached Storage (NAS) each provide high capacity file storage. For the following list, indicate whether the list item is more characteristic of a SAN or a NAS configuration.

a. High capacity file storage is directly attached to the network.
b. The data is accessed through a gateway server.
c. Fault tolerance is possible by wide area networking of mirrored sites.
d. Useful for distributing images of client computers.
e. Dedicated switch localizes LAN traffic to avoid performance problems when large volumes of data are being transferred.